ComplyIT365 — ITSM, GRC and third-party risk in one compliance operations platform
ComplyIT365 brings IT service management, governance, risk and compliance, vendor risk and asset management into one platform. Incidents, changes, assets and vendor reviews are recorded once and automatically linked to the controls they satisfy.
Everything your IT team needs.
Everything your auditors expect.
Two integrated suites — one for running IT operations, one for managing compliance — sharing the same data, same evidence, same platform.
Incident Management
Log, triage, escalate, and close incidents with SLA tracking and automatic audit trails — every action timestamped and linked to controls.
Service Request Management
Your IT front door. Manage service requests, approvals, and fulfilment through a published service catalogue — with full SLA visibility per request type.
Change Management
Structured RFC workflows with CAB approval, risk scoring, and rollback planning. Every change is a documented, reviewable event.
Release Management
Plan, schedule, and track releases with deployment checklists and post-release validation — keeping change and compliance tightly coupled.
Problem Management
Root cause analysis, known error database, and problem-to-incident linking to eliminate recurring issues before they become audit findings.
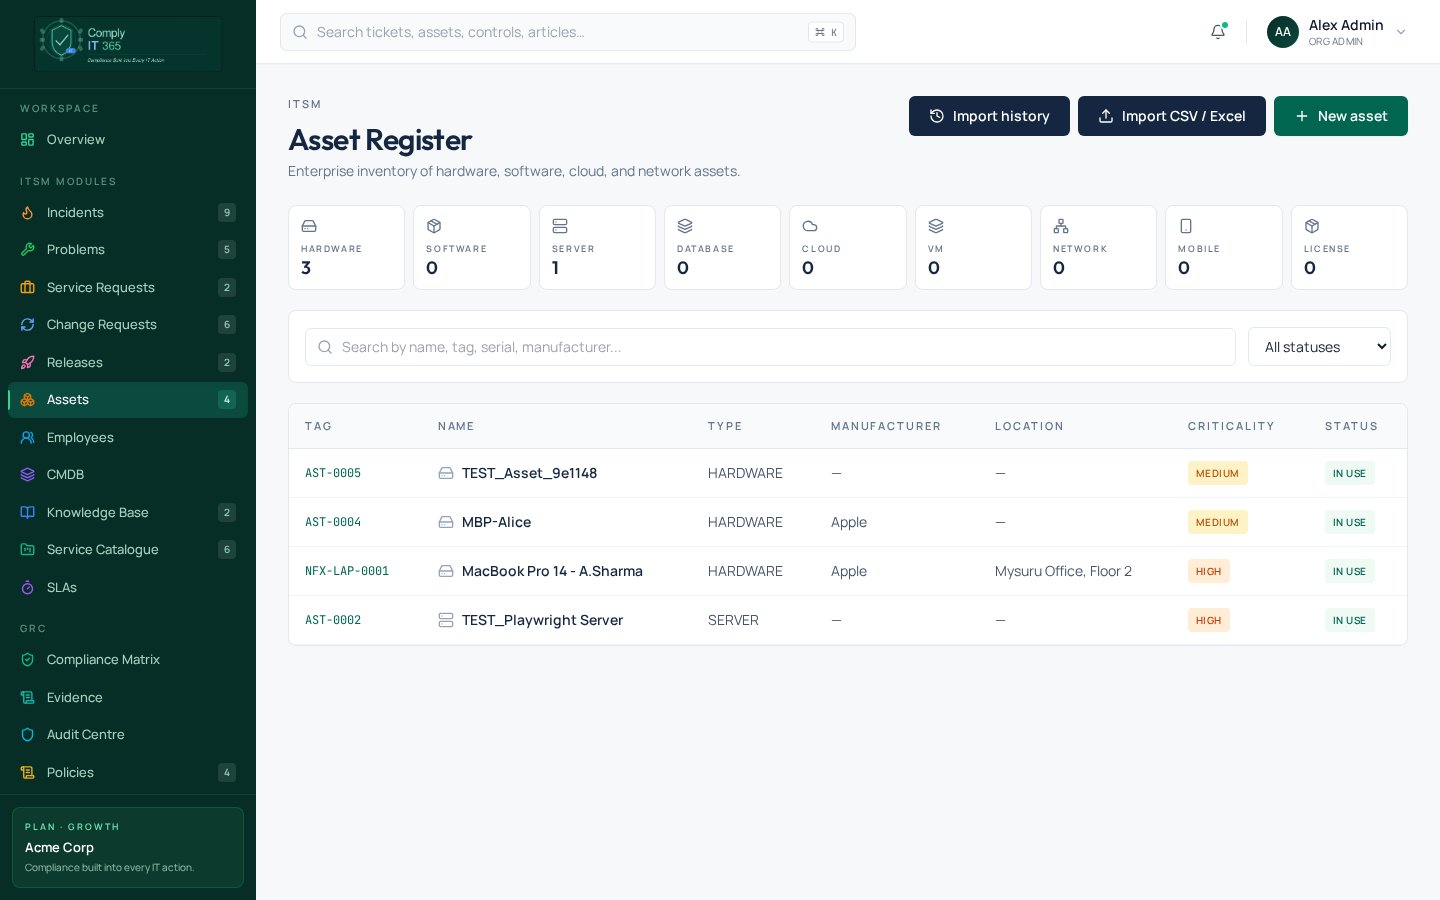
Asset Register
Maintain a live inventory of hardware, software, and cloud assets. Link assets to owners, risks, and controls for end-to-end traceability.
SLA & Service Catalogue
Define what you promise and prove you delivered it. Service definitions, response and resolution targets, and SLA breach visibility — all audit-visible.
Incident, problem, change, release, service request and SLA management with email-to-ticket routing.
Compliance matrix, controls, evidence, policies, risk register and an audit centre.
Vendor register, risk tiering, questionnaires, a secure vendor portal and an evidence ledger.
Asset register, CMDB relationships, employee assignments and asset audits.
Designed for the team that does
both IT ops and compliance
Most ITSM tools treat compliance as a bolt-on. We built it in from the schema up.
Unified Evidence Collection
Every ticket, change, and asset action automatically generates compliance evidence. No separate export step, no manual copy-paste into audit folders.
Control-Linked Workflows
Map your ITSM processes to specific SOC 2 criteria or ISO 27001 controls. When a process runs, it satisfies a control. Simple cause, clear effect.
Live Compliance Posture
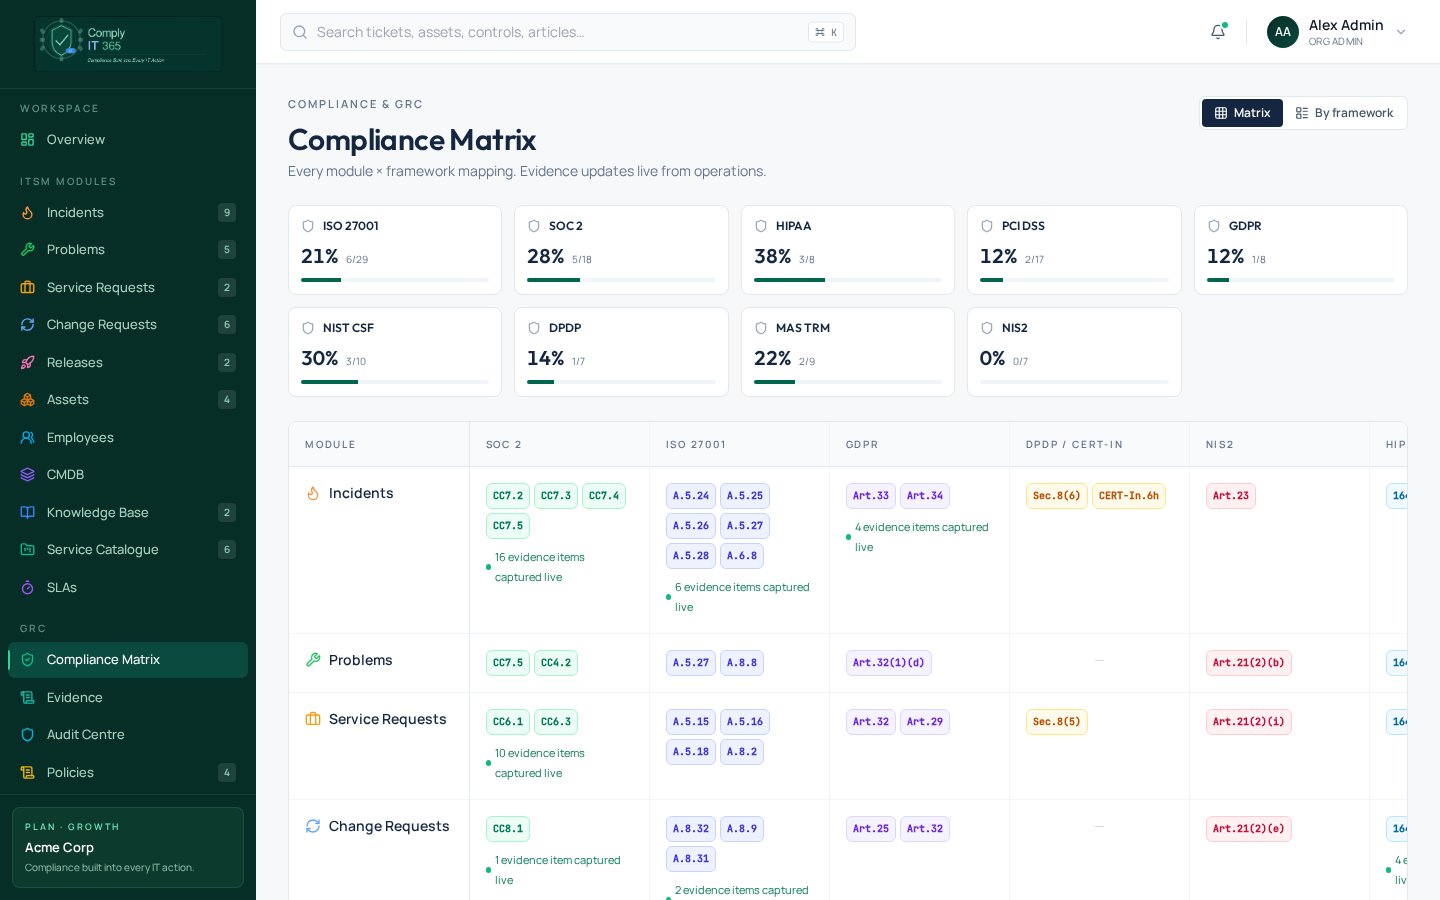
See control coverage per framework in the compliance matrix and open any control to the incidents, changes, assets and evidence behind it.
Role-Based Access, Natively
IT Ops, GRC leads, and external auditors each get a tailored view. Evidence access without exposing operational data. Least privilege by design.
Pick your Regpacks.
Ship compliance on day one.
ComplyIT365 ships with 16 pre-mapped Regpacks so you're never starting from a blank spreadsheet. Every control is wired to platform actions — one action can satisfy multiple frameworks at once.
Track coverage per framework in the compliance matrix, updated from live operations.
One platform, three tailored lenses
Analysts run operations. GRC leads own posture. Auditors verify evidence. Same data, right view — each persona sees the workflow and controls that matter to them.
Ship faster without a compliance detour
Log incidents, resolve tickets, and manage assets in one place — every action doubles as evidence automatically.
- Single-pane incident, request, change, problem, release workflows
- Personal queue with SLA timers and priority sorting
- Every ticket auto-links to the controls it satisfies — no extra effort
- Import assets from CSV/XLSX and start with a live inventory in minutes
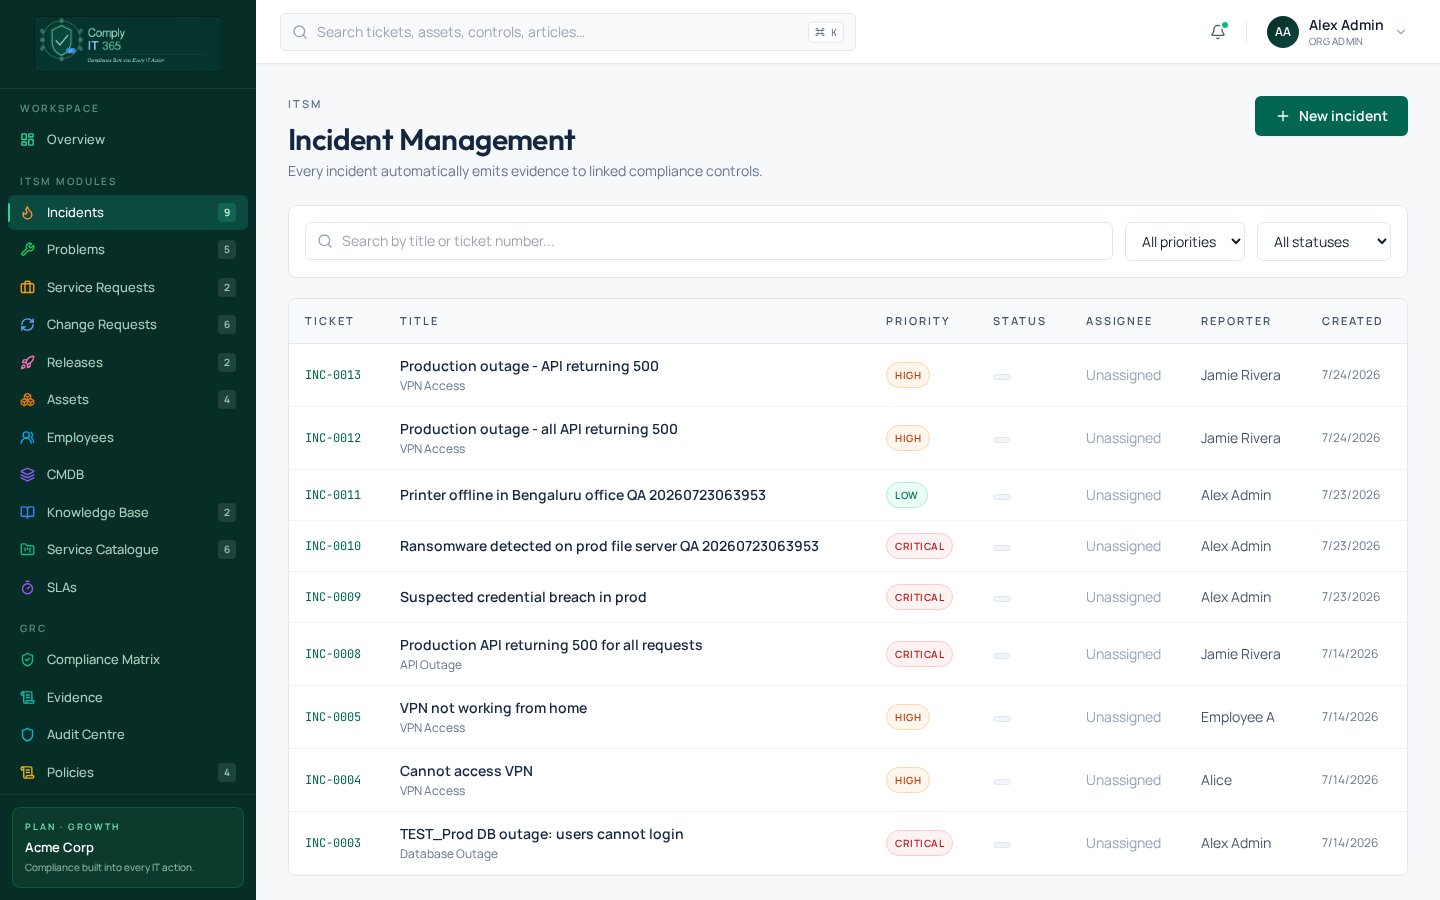
Analysts · Ship faster without a compliance detour
Log incidents, resolve tickets, and manage assets in one place — every action doubles as evidence automatically.
- Single-pane incident, request, change, problem, release workflows
- Personal queue with SLA timers and priority sorting
- Every ticket auto-links to the controls it satisfies — no extra effort
- Import assets from CSV/XLSX and start with a live inventory in minutes
GRC Leads · Multi-framework posture, one live matrix
See exactly where you stand against every Regpack. Which controls are covered, which need attention, which are backed by real evidence.
- Module × Framework matrix — SOC 2, ISO 27001, DPDPA, NIS2, HIPAA, PCI DSS, MAS TRM, NIST CSF, more
- Live control coverage % — auto-updated whenever operations run
- Risk register, vendor risk, and assessment gaps side-by-side
- Assign owners and set review dates for every control
Auditors · Evidence at your fingertips
A read-only, audit-scoped view of every control — with the linked incidents, changes, assets, policies, and evidence artifacts already attached.
- One click from a control → all supporting evidence with timestamps
- Immutable audit trail on every change, assignment, and status update
- Least-privilege access — auditors see what they need, nothing they don't
- Read-only auditor role scoped to controls and their evidence
Compliance shouldn't be a
separate team's problem
When your ITSM and your GRC tool are different systems, evidence collection becomes a full-time job. We fix the root cause.
- Evidence collected automaticallyIT actions = compliance evidence. No dual-entry, no post-hoc documentation sprints before your audit.
- One platform, two audiencesIT Ops teams see their workflows. GRC leads see their controls. Auditors see their evidence. Same data, right lens.
- Startup-friendly, enterprise-gradePriced for growth-stage companies pursuing their first SOC 2 or ISO cert — not just for teams with a dedicated GRC headcount.
- Deep Indian regulatory awarenessDPDP Act, RBI IT controls, SEBI compliance — built with Indian-context requirements from the start, not as an afterthought.
Priced around your programme,
not per-seat guesswork
Every ComplyIT365 deployment is scoped to your Regpacks, headcount, and hosting choice. We'll build a proposal that fits — no hidden add-ons, no audit-day surprises.
For pricing, please reach out to us at sales@complyit365.com.
Let's talk about your
compliance journey
Whether you're six months from your first SOC 2 audit or scaling a mature GRC programme, we'd love to understand where you are.
Talk to our team
We're practitioners who've been on both sides of the audit table — as auditors and as the team being audited. We'll give you an honest assessment, not a sales pitch.
Design partners get direct roadmap influence
We're onboarding a small number of design partners for our paid pilot programme. You'll get hands-on access, direct team support, and influence over the roadmap.
The app itself,
not a stock screenshot
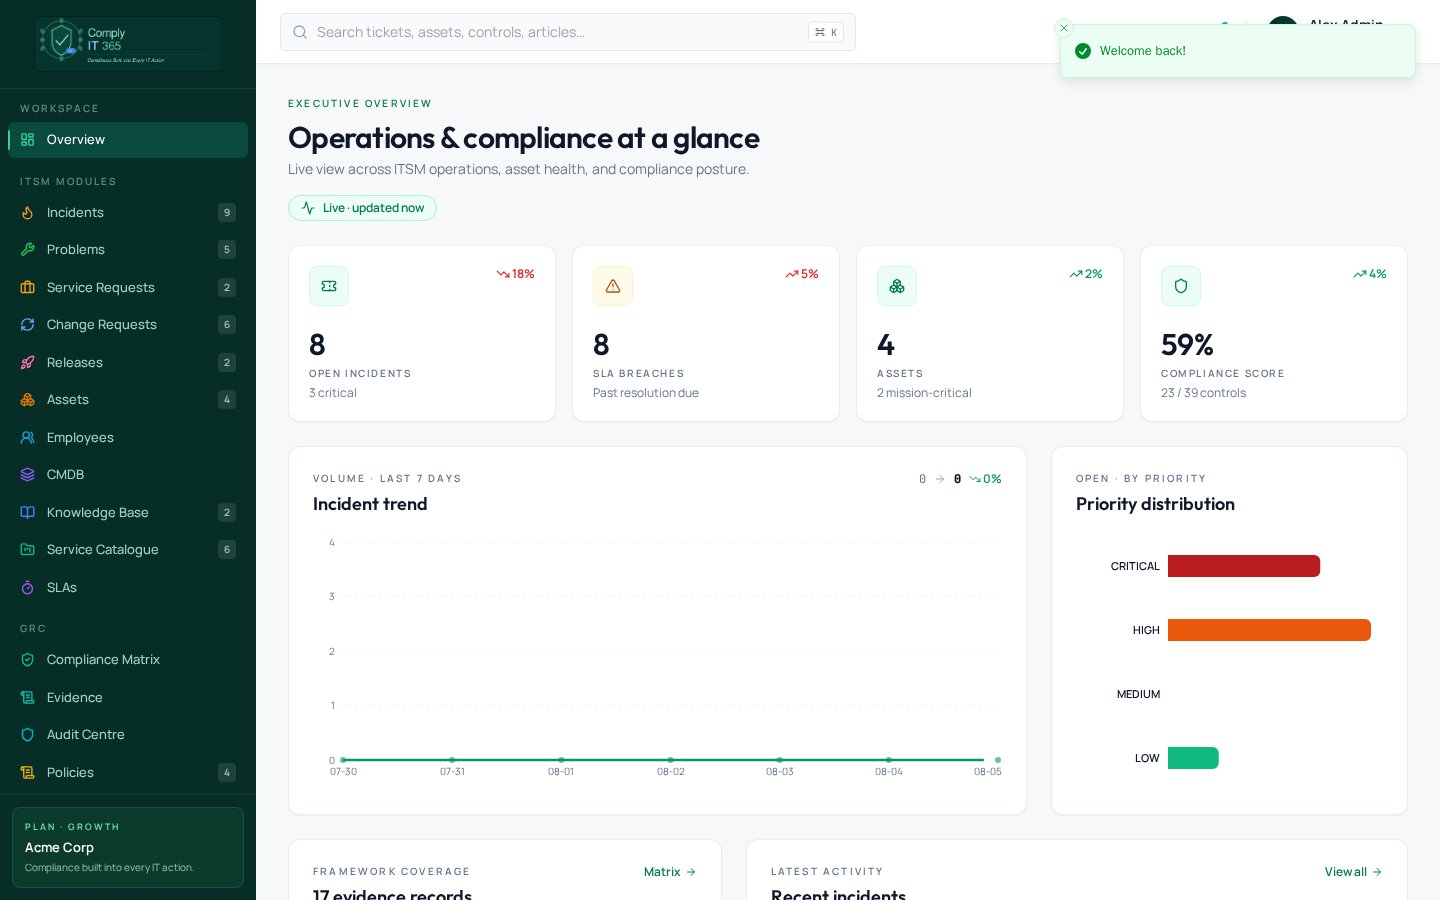
Real screens from ComplyIT365 — where your IT operations meet your evidence-of-record. Every action logged, every control tracked, every framework mapped.